Defence Contracts 2026 Comparisons
Contributed By Schiefer Rechtsanwälte GmbH
Law and Practice
Authors
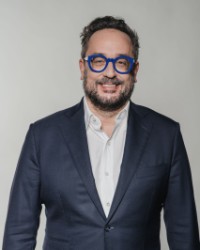
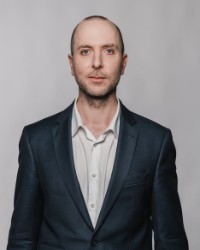
Schiefer Rechtsanwälte GmbH is an Austrian law firm with offices in Vienna and other major cities in Austria, focused on public procurement, defence and dual-use, and banking and finance. The firm advises contracting authorities, bidders, privately-owned companies and credit institutions across the full project life cycle, from strategy and tender design through award to contract performance and review proceedings. In the defence sector, the firm advises on major equipment programmes, government-to-government arrangements, industrial co-operation and security-of-supply structures, as well as on the export control, sanctions and investment screening questions arising in defence supply chains. Recent work includes acting as lead adviser on the industrial co-operation programme of Austria with Italian defence contractor Leonardo. The firm publishes regularly on procurement, defence regulation and defence financing.
1. Overview of the Defence Regulatory Framework
1.1 Principal Legislation and Regulatory Framework
The constitutional frame is set by Article 9a of the Federal Constitutional Act (Bundes-Verfassungsgesetz, B-VG), which establishes the principle of comprehensive national defence, and by the Federal Constitutional Act on the Neutrality of Austria of 1955 (Neutralitätsgesetz), which enshrines permanent neutrality and shapes the entire defence regulatory landscape.
The key statutes are:
- the Defence Act 2001 (Wehrgesetz 2001) and the Military Powers Act (Militärbefugnisgesetz, MBG) on the organisation and powers of the Austrian Armed Forces (Bundesheer);
- the Federal Procurement Act 2018 (Bundesvergabegesetz 2018, BVergG 2018) as the general procurement framework and the Federal Procurement Act for Defence and Security 2012 (Bundesvergabegesetz Verteidigung und Sicherheit 2012, BVergGVS 2012), implementing Directive 2009/81/EC (the “Defence Procurement Directive”);
- the War Material Act (Kriegsmaterialgesetz, KMG) and the Foreign Trade Act 2011 (Außenwirtschaftsgesetz 2011, AußWG 2011), together with Regulation (EU) 2021/821 (the “EU Dual-Use Regulation”), for export controls;
- the Sanctions Act 2024 (Sanktionengesetz 2024, SanktG 2024) for the implementation of UN and EU sanctions;
- the Investment Control Act (Investitionskontrollgesetz, InvKG) for foreign direct investment (FDI) screening;
- the Information Security Act (Informationssicherheitsgesetz, InfoSiG) and the Information Security Regulation for classified information; and
- the Network and Information System Security Act 2026 (Netz- und Informationssystemsicherheitsgesetz 2026, NISG 2026), applicable from 1 October 2026, for cybersecurity.
1.2 Competent Authorities
The key government ministries responsible for overseeing defence in Austria are the following:
- Federal Ministry of Defence (Bundesministerium für Landesverteidigung, BMLV): Responsible for the armed forces, defence procurement through its armaments and procurement directorates, facility security clearances for classified defence contracts, and the military intelligence services (Heeresnachrichtenamt and Abwehramt).
- Federal Ministry for Economy (Bundesministerium für Wirtschaft, Energie und Tourismus, BMWET): Grants export licences for military and dual-use goods under the Foreign Trade Act 2011, conducts FDI screening under the Investment Control Act and is responsible for defence industry policy.
- Federal Ministry of the Interior (Bundesministerium für Inneres, BMI): Grants war material licences under the War Material Act in agreement with the foreign affairs and defence ministries, and hosts the Directorate for State Protection and Intelligence (Direktion Staatsschutz und Nachrichtendienst, DSN) and, from October 2026, the new Federal Office for Cybersecurity.
- Federal Ministry of Finance (Bundesministerium für Finanzen, BMF): Controls the defence budget via the annual Federal Finance Act and the medium-term expenditure framework, oversees the customs administration including the tariffs authority, and owns the central purchasing body in Austria (Bundesbeschaffung GmbH, BBG), through which non-military-specific procurement is channelled.
Other Authorities
The Federal Ministry for European and International Affairs (Bundesministerium für europäische und internationale Angelegenheiten, BMEIA) provides the foreign and security policy assessment for licensing and embargo matters. The Austrian Customs Office (Zollamt Österreich) enforces export controls at the border. The Financial Market Authority (Finanzmarktaufsicht, FMA) has supervised financial sanctions compliance since 1 January 2026, having taken over from the Oesterreichische Nationalbank. The Federal Administrative Court (Bundesverwaltungsgericht, BVwG) reviews procurement decisions. Public prosecutors, including the Economic Crime and Corruption Prosecutor’s Office (Wirtschafts- und Korruptionsstaatsanwaltschaft, WKStA), handle criminal enforcement. The ministries interact through statutory agreement (Einvernehmen) requirements, most visibly in war material licensing.
1.3 Definition of “Defence” and “Dual-Use”
“War material” (Kriegsmaterial) is defined by the War Material Regulation issued under the War Material Act and covers weapons, munitions and equipment specifically designed or adapted for combat use. It triggers the strictest licensing regime.
Military or defence goods in the broader sense are defined under the Foreign Trade Act 2011 by reference to the EU Common Military List and include defence-related products within the meaning of Directive 2009/43/EC (the “Transfers Directive”). For procurement purposes, the Federal Procurement Act for Defence and Security 2012 refers to military equipment on the basis of the Council list of 1958 read together with the Common Military List.
Dual-use items are defined by Article 2 of the EU Dual-Use Regulation as items, including software and technology, that can be used for both civil and military purposes; the control list is Annex I of that Regulation. The practical consequence of the layered definitions is that war material falls under the War Material Act, other military goods under the Foreign Trade Act 2011, and dual-use items under the directly applicable EU Regulation as supplemented by national provisions.
1.4 International Frameworks and Treaty Obligations
EU law is the dominant layer, more specifically:
- the Defence Procurement Directive;
- the Transfers Directive on intra-EU transfers;
- the EU Dual-Use Regulation; and
- Common Foreign and Security Policy (CFSP) sanctions regulations,
which apply directly or through implementing statutes.
Austria is not a NATO member due to its permanent neutrality, but it has participated in the Partnership for Peace since 1995 and takes part in the EU’s Common Security and Defence Policy, in PESCO projects and in the European Defence Agency. Since 2023, Austria has participated in the European Sky Shield Initiative for joint air defence procurement, framed by the government as compatible with neutrality.
UN Security Council resolutions, including arms embargoes, are implemented through EU law and the Sanctions Act 2024. Austria ratified the Arms Trade Treaty in 2014, is a founding participant of the Wassenaar Arrangement, whose secretariat is seated in Vienna, and participates in the Missile Technology Control Regime, the Australia Group, the Nuclear Suppliers Group and the Zangger Committee. Austria also has a strong humanitarian arms control profile, including the Anti-Personnel Mine Ban Convention, the Convention on Cluster Munitions and the Treaty on the Prohibition of Nuclear Weapons, of which Austria was a driving force.
2. Procurement and Government Contracts in the Defence Sector
2.1 Defence Procurement Legislation
Austria has a bespoke defence procurement regime: the Federal Procurement Act for Defence and Security 2012 implements the Defence Procurement Directive and governs contracts for military equipment, sensitive equipment and related works and services, as well as works and services for specifically military purposes or involving classified information. The Federal Procurement Act 2018 remains the general framework and applies to non-sensitive purchases by defence authorities.
The exemptions mirror those of the Directive: the “essential security interests” carve-out of Article 346 of the Treaty on the Functioning of the European Union (TFEU); contracts governed by international rules; government-to-government contracts; contracts for intelligence activities; contracts awarded in third countries during deployments; and certain research and development services. In line with the case law of the CJEU, exemptions are interpreted narrowly and the burden of justification lies with the contracting authority. Below the EU thresholds, a lighter national regime within the Federal Procurement Act for Defence and Security 2012 applies.
2.2 Contracting Authorities and Entities Subject to Defence Procurement Rules
The regime applies to contracting authorities in the functional sense, namely, the Federation, the regions, municipalities and bodies governed by public law, as well as sector contracting entities for defence-relevant purchases. In practice, the dominant buyer is the Federal Ministry of Defence; the Federal Ministry of the Interior and other federal bodies award security-sensitive contracts – for example, in policing and civil protection.
State-owned enterprises are covered where they qualify as bodies governed by public law or as sector contracting entities. Private entities are caught where they act as central purchasing bodies or where a subsidised contract falls within the statute; purely private purchases are not covered. Since defence procurement is federal, review competence lies with the Federal Administrative Court regardless of which ministry is the procurer.
2.3 Types of Contracts and Value Thresholds
The contract types covered are those concerning the supply of military and sensitive equipment, including parts and components; works and services directly related to such equipment across its entire life cycle; works and services for specifically military purposes; and sensitive works and services. Research and development is covered only in limited constellations; R&D services where the contracting authority does not exclusively retain the benefits are exempt.
The EU thresholds applicable from 1 January 2026 under Commission Delegated Regulation (EU) 2025/2487 are EUR432,000 for supply and service contracts and EUR5,404,000 for works contracts. Below these values, national procedures with reduced formal requirements apply, including direct awards below the national de minimis limits.
2.4 Restricted and Classified Procurement
The Federal Procurement Act for Defence and Security 2012 allows contracting authorities to impose security-of-information requirements: bidders must demonstrate their ability to protect classified information, typically through a facility security clearance under the Information Security Act framework and individual clearances for the personnel involved (reliability checks in the military domain, security screenings by the Directorate for State Protection and Intelligence in the civilian domain). The commitments flow down to subcontractors through security annexes.
Where the contract itself is classified or a formal procedure would compromise essential security interests, the procurement can be exempted altogether under Article 346, TFEU and is then conducted outside the statute under internal rules. International classified contracts follow the applicable bilateral security-of-information agreements.
2.5 Tender Procedures for Defence Contracts
Under the Federal Procurement Act for Defence and Security 2012, the restricted procedure and the negotiated procedure with prior publication are available without special justification; an open procedure does not exist under the defence regime. The competitive dialogue process is available for particularly complex projects, and the negotiated procedure without prior publication only on enumerated grounds.
In practice, negotiated procedures dominate, because requirements, security arrangements and long-term support need to be negotiated. In recent years, major platform programmes have frequently been implemented through government-to-government arrangements or joint procurement with partner states, which are exempt from the Defence Procurement Directive. Direct awards are therefore considerably more common in the defence context than in general public procurement.
2.6 Direct Contract Awards and Single-Source Procurement
The negotiated procedure without prior publication is available in particular for: extreme urgency resulting from a crisis; technical reasons or exclusive rights that make one supplier the only possible source; additional deliveries by the original supplier where a change of supplier would cause disproportionate technical difficulties, which covers interoperability concerns; and certain R&D and commodity situations. In addition, Article 346 TFEU permits a full derogation where essential security interests genuinely so require, and government-to-government contracts are exempt.
Austria has no dedicated single-source pricing or profit regulation comparable to the US or UK regimes. Price reasonableness is addressed through negotiation and contract design, budgetary law and ex-post audits by the Court of Audit (Rechnungshof).
2.7 Offsets, Industrial Participation and Sovereign Capability Requirements
Austria imposes no statutory offset obligations. The earlier administrative practice of requiring offsets (Gegengeschäfte) for major defence purchases, most prominently in the Eurofighter programme, was discontinued in the mid-2010s following EU-law concerns and audit criticism.
In 2025, Austria concluded its first industrial co-operation arrangement since then, with the Italian Leonardo group. Schiefer Rechtsanwälte advised on the structuring of the co-operation, which is designed to comply with EU law and national law. Implementation is currently under way, and the arrangement may serve as a template for industrial co-operation in future procurement programmes.
The structuring question in arrangements of this kind is which contributions may be credited. In the case of the Eurofighter offsets, the audit criticism concerned transactions that would have taken place in any event and multipliers that produced credited amounts without a counterpart in Austrian value creation. Current practice therefore should rest on additionality, ie, on transactions that would not have taken place without the arrangement. Beyond such negotiated arrangements, industrial participation may only be pursued within the narrow limits of EU law: through security-of-supply and information-security requirements under the Federal Procurement Act for Defence and Security 2012, or where a genuine Article 346, TFEU justification exists. Sovereign capability considerations increasingly appear in programme design – for example, in-country maintenance, ammunition supply and long-term support. The policy debate on strengthening domestic and European value creation in defence procurement has intensified with the EU’s defence-industrial agenda under the European Defence Industry Programme (EDIP).
2.8 Security of Supply and Resilience Requirements
Security of supply is an express feature of the defence regime. Contracting authorities may require bidders to certify and commit to, among other things: disclosure of the supply chain and the location of production; the ability to meet surge and crisis demands; assurances regarding export and transit authorisations from the bidder’s home state; and continuity of maintenance, modernisation and spare parts over the life cycle. These commitments become contract terms and are enforced through ordinary contractual remedies, retention mechanisms and termination rights.
Complementary instruments exist outside individual contracts: the Defence Funding Act (Landesverteidigungs-Finanzierungsgesetz) provides multi-year budget certainty, the Federal Crisis Security Act (Bundes-Krisensicherheitsgesetz) establishes crisis co-ordination structures, and NIS-2 (Directive (EU) 2022/2555) duties will add supply chain security obligations from October 2026.
2.9 Evaluation Criteria and Award of Defence Contracts
Contracts are awarded to the most economically advantageous tender or, exceptionally, on lowest price; in defence, best-value awards with substantial non-price weighting are standard. Typical criteria include technical performance, quality, the logistics and support concept, delivery schedule, life cycle costs, interoperability with existing systems and partner forces, and security of supply.
National industrial base preferences cannot lawfully be used as award criteria under EU law; security-of-supply criteria may, however, legitimately reflect supply chain resilience and support arrangements. Whole-life costing is expressly recognised in Austrian procurement law and is increasingly used for platforms with long service lives.
2.10 Exclusion Grounds
The exclusion grounds broadly track general procurement law: mandatory exclusion for final convictions for participation in a criminal organisation, corruption, fraud, terrorist offences or money laundering, and discretionary grounds such as insolvency, grave professional misconduct or misrepresentation.
The defence regime adds specific grounds: a bidder may be excluded where it does not possess the reliability necessary to exclude risks to national security, which may be established by any means of evidence, including protected data sources; the failure to obtain required security clearances is in practice decisive. Sanctions law adds a further layer: awards to listed persons are prohibited, and Article 5k of Council Regulation (EU) No 833/2014 bans awards to Russian entities and to bidders relying on Russian subcontractors for more than 10% of the contract value.
2.11 Transparency and Confidentiality
Above-threshold procedures require EU-wide contract notices and contract award notices via Tenders Electronic Daily (the official online database of the EU for publishing such notices), and the core contract data of federal awards are published. The defence regime, however, permits withholding information whose release would impede law enforcement, harm legitimate commercial interests or prejudice security interests; classified elements are not published at all.
The Freedom of Information Act (Informationsfreiheitsgesetz), in force since 1 September 2025, replaced official secrecy with a general right of access to information, subject to exceptions that include national security and defence, so defence contracts remain largely shielded from individual access requests and can only be published heavily redacted (if they must be published at all). Oversight is exercised primarily by the Court of Audit and parliamentary committees rather than through public disclosure.
2.12 Modification and Termination of Defence Contracts
The modification of defence contracts follows the general regime: modifications are permissible without a new procedure where they are provided for in clear review clauses, concern additional necessary supplies or services within value limits, respond to unforeseeable circumstances, or are non-substantial. Substantial modifications require a new award procedure and expose the parties to ineffectiveness claims.
As regards termination, the legislation requires that contracts can be terminated where the contractor should have been excluded at the time of award or where the contract was awarded in serious breach of EU law. Beyond that, termination is governed by the contract and general civil law; there is no statutory government right of termination for convenience. Such rights are, however, frequently stipulated in defence contracts, combined with negotiated compensation mechanisms.
2.13 Challenging Defence Procurement Decisions
Undertakings with an interest in a specific contract that face or have suffered damage may challenge decisions of federal contracting authorities before the Federal Administrative Court; its decisions are subject to review by the Supreme Administrative Court and the Constitutional Court. Before award, separately challengeable decisions can be set aside within short deadlines, generally ten days, and interim relief is available; after award, declaratory proceedings can lead to ineffectiveness of the contract or alternative sanctions. Damages are pursued before the civil courts and require a prior declaratory finding.
There is no general national-security carve-out from review. Where a contract was awarded outside the statute – for example, under Article 346, TFEU or as a government-to-government contract – the review bodies examine whether the exemption was lawfully invoked, applying the strict standards developed by the CJEU.
3. Export Controls and Dual-Use Items
3.1 Export Control Legislation and Regulatory Framework
The export control framework rests on three pillars.
- First, the War Material Act governs war material – import, export and transit require a licence from the Federal Minister of the Interior in agreement with the foreign affairs and defence ministers.
- Second, the Foreign Trade Act 2011, together with the Foreign Trade Regulation (Außenwirtschaftsverordnung), governs other military goods, defence-related products under the Transfers Directive, technical assistance, brokering and transit, and is administered by the Federal Ministry for Economy.
- Third, the EU Dual-Use Regulation applies directly to dual-use items and is supplemented by the Foreign Trade Act 2011.
Customs enforcement lies with the Austrian Customs Office, while criminal enforcement lies with the public prosecutors and courts. Nuclear material is additionally covered by the Safeguards Act (Sicherheitskontrollgesetz).
3.2 Scope of Controls: Military and Dual-Use Lists
Three control lists apply:
- the war material list under the War Material Regulation;
- the military list annexed to the Foreign Trade Regulation, which mirrors the EU Common Military List and thereby the Wassenaar Munitions List; and
- the dual-use list in Annex I of the EU Dual-Use Regulation, which is updated annually by a Commission Delegated Regulation to reflect decisions of the Wassenaar Arrangement, the Missile Technology Control Regime, the Australia Group and the Nuclear Suppliers Group.
Austria participates in all major multilateral regimes and hosts the Wassenaar Arrangement secretariat in Vienna. The Foreign Trade Regulation additionally contains a limited number of national control items. Classification follows EU practice; binding classification guidance can be sought from the Federal Ministry for Economy.
3.3 Licence Requirements
For war material under the War Material Act, only individual licences exist, for each import, export or transit.
For military and dual-use goods under the Foreign Trade Act 2011 and the EU Dual-Use Regulation, the main categories are: individual licences for a single end-user or transaction; global licences covering multiple end-users or destinations for a defined product range, typically conditional on an internal compliance programme; and general licences, including the EU General Export Authorisations EU001 to EU008 for low-risk destinations and scenarios, plus national general licences. Certification as a recipient of defence-related products enables simplified intra-EU transfers under the Transfers Directive. Brokering, technical assistance and transit are subject to their own authorisation types. The appropriate instrument depends on destination risk, product sensitivity and transaction frequency.
3.4 Licence Application Process
Applications are filed electronically with the Federal Ministry for Economy for military and dual-use goods and with the Federal Ministry of the Interior for war material. Required documentation includes a precise technical description and classification of the items, the underlying contracts or orders, end-use and end-user certificates, the shipping route and, for global licences, a description of the internal compliance programme.
Inter-ministerial consultation is standard: the Federal Ministry for European and International Affairs assesses the foreign policy criteria, and the Federal Ministry of Defence is involved where relevant; for war material, the statutory agreement requirement between the ministries applies. Straightforward dual-use individual licences are typically processed within a few weeks; applications concerning sensitive destinations or war material can take several months. Early pre-application engagement with the relevant authority is advisable for complex programmes.
3.5 Criteria for Granting or Refusing Licences
For war material, the War Material Act prohibits licences in particular where the goods would be delivered into areas of armed conflict or in imminent danger of such conflict, where there is reason to believe that they would be used to suppress human rights, or where Austria’s international obligations, including embargoes, or its foreign policy interests, shaped by permanent neutrality, would be infringed. These limits attach to deliveries from Austrian territory. Groups producing in several countries therefore decide at an early stage from which site a given contract can be served, which makes this a question of structuring rather than a general bar on the business.
For military and dual-use goods, the assessment incorporates the eight criteria of Common Position 2008/944/CFSP, including respect for human rights, the internal and regional situation, and the risk of diversion, as well as Articles 6 and 7 of the Arms Trade Treaty. In practice, the plausibility of the stated end use, the diversion risk and the recipient’s track record are the decisive points of the assessment.
3.6 End-User Controls and Post-Shipment Verification
End-user certificates are standard for military exports and for sensitive dual-use transactions; they typically contain end-use undertakings and re-export restrictions. Licences may be granted subject to conditions, including delivery verification documents.
Exporters must keep records for the statutory retention periods, verify their counterparties and report changes in relevant circumstances. The catch-all provisions of the EU Dual-Use Regulation oblige exporters to notify the authority where they are aware, or have grounds to suspect, that non-listed items are intended for a use connected with weapons of mass destruction or certain military end uses. Austria does not operate a broad on-site post-shipment inspection programme; verification relies primarily on documentation, licensing conditions and international co-operation.
3.7 Brokering and Intermediary Activities
Brokering of military goods is regulated by the Foreign Trade Act 2011: arranging or negotiating transactions in controlled goods between third countries requires an authorisation, and also in defined cases where the broker acts from abroad but is an Austrian national or resident. For dual-use items, brokering controls follow the EU Dual-Use Regulation where weapons-of-mass-destruction or military end-use concerns arise.
War material transactions touching Austrian territory require transit licences under the War Material Act. Technical assistance related to military and listed dual-use items is separately controlled. The penalties for unlicensed brokering mirror those for unlicensed exports.
3.8 Intra-Company and Intra-Group Transfers
There is no blanket intra-company or intra-group exemption. Intra-EU transfers of defence-related products benefit from the the simplified procedures introduced by the Transfers Directive as implemented in the Foreign Trade Act 2011: general and global transfer licences and the certification of recipient companies reduce transaction-level licensing. Most dual-use items circulate freely within the EU, with the exception of the particularly sensitive Annex IV items.
Transfers of controlled technology to group entities outside the EU are fully controlled, including intangible transfers by email, cloud access or technical support. Global licences and robust internal compliance programmes are the practical tools for managing recurring intra-group flows.
3.9 Enforcement, Penalties and Voluntary Disclosure
Breaches of export control legislation are criminal offences: the unlicensed export, import, transit or brokering of controlled goods under the Foreign Trade Act 2011 carries a penalty of imprisonment of up to three years, and substantially more in aggravated cases, in particular where weapons of mass destruction are concerned; violations of the War Material Act are likewise criminal offences. Legal entities face corporate fines under the Corporate Criminal Liability Act (Verbandsverantwortlichkeitsgesetz, VbVG). Lesser breaches of documentation and reporting duties are administrative offences. Enforcement involves the Austrian Customs Office and the public prosecutors.
There is no formal voluntary disclosure programme. Self-reporting, co-operation and remediation are, however, mitigating factors in sentencing and in the decision whether to prosecute an entity under the Corporate Criminal Liability Act, and they are expected by the licensing authority in order to preserve the reliability required for future licences.
4. Compliance, Sanctions and Embargoes
4.1 Sanctions Legislation and Regulatory Framework
EU sanctions regulations adopted under Article 215 TFEU apply directly in Austria. The Sanctions Act 2024, in force since February 2025, is the national framework statute: it enables the rapid implementation of UN listings, allocates competences and contains penal provisions; and it applies subsidiarily to the Foreign Trade Act 2011, the War Material Act and the Safeguards Act.
Competences are divided: the Financial Market Authority has supervised compliance by financial market participants since 1 January 2026, having taken over from the Oesterreichische Nationalbank; the Federal Ministry for Economy handles trade-related measures within the Foreign Trade Act 2011 framework; the Federal Ministry of Finance publishes national implementing acts; the Federal Ministry of the Interior supports enforcement; and the Federal Minister of Justice grants derogations for the award and continued performance of public contracts. Third-country measures such as US OFAC sanctions have no legal effect in Austria; Regulation (EC) No 2271/96 (the “EU Blocking Statute”) applies.
4.2 Arms Embargoes
Austria implements all UN Security Council arms embargoes as well as autonomous EU embargoes. They operate through directly applicable EU regulations and through mandatory licence refusals under the War Material Act and the Foreign Trade Act 2011. Prohibited activities typically include the supply of arms and related materiel, related technical assistance, brokering and financing to embargoed destinations or entities. The Russia regime additionally bans a wide range of dual-use and advanced-technology exports.
Exceptions exist for each regime, typically for humanitarian purposes or protective equipment for personnel of international organisations and media, and require authorisation. Independently of any embargo, the War Material Act bars war material exports into areas of armed conflict, an Austrian particularity rooted in neutrality.
4.3 Screening and Due Diligence Requirements
There is no express statutory screening duty for non-financial companies. However, the prohibitions on making funds or economic resources available to listed persons make counterparty screening a practical necessity, and its absence will be treated as negligence in enforcement. Financial market participants must maintain sanctions-related policies, controls and procedures, supervised by the Financial Market Authority, which applies the EBA guidelines on restrictive measures.
Ownership and control are assessed in line with the EU Best Practices: a 50% ownership presumption, control indicators and aggregation of the holdings of several listed persons. Defence sector participants must additionally check their subcontractor chains, notably against the prohibition in Article 5k of Council Regulation (EU) No 833/2014 on Russian subcontractors above 10% of contract value in public procurement.
4.4 Licences, Derogations and Exceptions
Each EU regime provides derogation grounds – for example, basic needs, legal fees, prior contracts and humanitarian activities. Austrian competence is split: the Financial Market Authority authorises the release of frozen funds held by financial market participants and related transactions; the Federal Ministry for Economy grants trade derogations within the Foreign Trade Act 2011 framework; and the Federal Minister of Justice authorises the award and the continued performance of public contracts and concessions affected by sanctions. Residual competences follow the Sanctions Act 2024.
Applications must evidence the derogation ground precisely and document the payment and delivery flows. Processing times vary considerably by regime and complexity, and no part of the transaction may be implemented before the authorisation has been granted.
4.5 Extraterritorial Sanctions and Secondary Sanctions Risk
Austria does not recognise or give effect to extraterritorial third-country sanctions. The EU Blocking Statute prohibits compliance with the listed US measures and provides for the non-recognition of related judgments; breaches are penalised under national administrative penal law.
The practical reality for defence groups is nonetheless significant US exposure through ITAR- and EAR-controlled components, US dollar clearing and US persons within the organisation. Risk management typically includes mapping the US nexus of products and transactions, tracking licence conditions attached to US-origin content, drafting sanctions clauses so that they remain compatible with the EU Blocking Statute, and establishing escalation procedures for situations of conflicting obligations.
4.6 Sanctions Compliance Programmes
An effective programme for a defence sector participant should include: clear management responsibility and a designated sanctions officer; a documented risk assessment by business line, geography and product; counterparty and payment screening with sensibly calibrated matching; end-user and end-use due diligence integrated with the export control process; contractual protections, including no-re-export clauses, and audit rights; training; escalation, reporting and record-keeping; and periodic independent review. Integrating sanctions, export control and procurement-exclusion checks into one due diligence process is best practice in the defence sector.
Guidance exists on several levels: Financial Market Authority communications and the EBA guidelines for financial market participants, the European Commission’s recommendation on internal compliance programmes for dual-use trade, and the Federal Ministry for Economy’s requirement for an internal compliance programme as a condition for global export licences.
4.7 Enforcement, Penalties and Voluntary Disclosure
Sanctions breaches are criminal offences prosecuted before the ordinary courts and can lead to imprisonment and forfeiture; legal entities are liable under the Corporate Criminal Liability Act. Directive (EU) 2024/1226 obliges EU member states to criminalise defined violation and circumvention conduct with maximum penalties of at least five years’ imprisonment for serious cases; the status of its implementation into Austrian law should be verified at the time of reading. Supervisory breaches by financial market participants attract administrative penalties imposed by the Financial Market Authority.
There is no formal self-disclosure or leniency mechanism for sanctions matters. Voluntary disclosure, co-operation and remediation are taken into account as mitigating factors in sentencing, in corporate liability proceedings and in the authorities’ exercise of discretion, while the duration of the breach, concealment and senior management involvement are aggravating factors.
4.8 Recent Enforcement Actions and Developments
The most significant recent institutional development is the transfer of financial sanctions supervision to the Financial Market Authority on 1 January 2026, with an expanded scope covering insurers, investment firms and crypto-asset service providers and stronger on-site inspection powers. On the substantive side, the successive EU packages against Russia through 2025 tightened export restrictions, targeted circumvention via third countries and expanded the contractual no-re-export obligations.
Austrian enforcement attention has focused on circumvention structures and on the administration of freezing measures. Court statistics on sanctions prosecutions remain limited, and investigations are typically not publicised.
5. National Security Regulation
5.1 National Security Legislation Applicable to the Defence Sector
There is no single national security statute; instead, the framework is built from several layers.
- Article 9a of the Federal Constitutional Act establishes comprehensive national defence.
- The Defence Act 2001 and the Military Powers Act govern the armed forces and military security powers, including the military intelligence services (Heeresnachrichtenamt and Abwehramt).
- The State Protection and Intelligence Service Act governs the Directorate for State Protection and Intelligence within the Federal Ministry of the Interior.
- The Information Security Act governs classified information.
- The Federal Crisis Security Act establishes crisis co-ordination structures and a federal situation centre.
The espionage and secrecy offences of the Criminal Code protect against intelligence activities to Austria’s detriment. The Network and Information System Security Act 2026 adds cybersecurity regulation from October 2026. Administration is spread across the Federal Ministry of Defence, the Federal Ministry of the Interior and the Federal Chancellery, with dedicated parliamentary oversight subcommittees for the intelligence services.
5.2 Security Vetting and Clearance Requirements
Two security clearance tracks exist. In the military domain, reliability checks (Verlässlichkeitsprüfungen) under the Military Powers Act are conducted by the Abwehramt for persons with access to military installations or classified material. In the civilian domain, security screenings are conducted by the Directorate for State Protection and Intelligence under the state protection framework. The depth of vetting is graduated in line with the classification levels.
Companies performing classified contracts require a facility security clearance under the Information Security Act framework, administered for defence contracts by the Federal Ministry of Defence; the personnel concerned receive individual clearances. Checks require the consent of the person concerned, and they involve registry and intelligence queries and, at higher levels, extended vetting. Clearances are time-limited and can be revoked at any time where the underlying reliability ceases to exist.
5.3 Classified Information and Official Secrets
The Information Security Act and the Information Security Regulation govern classified information, with four levels: restricted (Eingeschränkt), confidential (Vertraulich), secret (Geheim) and top secret (Streng Geheim). The core obligations are need-to-know access, personnel and facility clearances, physical and IT protection measures, registry handling and the flow-down of all requirements to subcontractors through security annexes to the contract.
Provisions of the Criminal Code sanction the disclosure of official secrets and intelligence offences to the detriment of Austria. International exchanges of classified information rest on bilateral security-of-information agreements and on Austria’s arrangements with the EU; equivalence tables map foreign classification levels to the Austrian ones.
5.4 Critical National Infrastructure and Defence Assets
Austria has no statutory list designating defence assets as critical national infrastructure. Protection is organised through the Austrian Programme for Critical Infrastructure Protection as a policy framework, the crisis structures of the Federal Crisis Security Act, and NIS legislation for the cyber dimension, with the Network and Information System Security Act 2026 replacing the Network and Information System Security Act 2018 from 1 October 2026. The implementation of the Critical Entities Resilience Directive (EU) 2022/2557 was still pending at the time of writing and should be verified.
Military installations enjoy specific protections under the Military Powers Act, including protected zones and security areas. Defence contractors are captured indirectly: through classified-contract requirements, through NIS-2 supply chain duties and through sector coverage where they also operate in listed sectors such as manufacturing or transport.
5.5 Cybersecurity Requirements for Defence Contractors
There is no Austrian equivalent of the US CMMC certification scheme. Cybersecurity requirements arise from three sources.
- First, for classified contracts, the technical and organisational requirements of the Information Security Regulation, verified in the facility clearance process.
- Second, from 1 October 2026, the Network and Information System Security Act 2026 for in-scope entities: registration by 31 December 2026, binding risk management measures, management accountability and training, and incident reporting within 24 hours (early warning) and 72 hours (incident notification), with fines of up to EUR10 million or 2% of worldwide turnover.
- Third, contractual requirements in tenders, where certification to ISO/IEC 27001 or equivalent standards is increasingly demanded. EU-funded projects under the European Defence Fund and EDIP impose additional programme-level security rules.
5.6 Supply Chain Security
There are no general statutory country-of-origin bans for defence supply chains. The relevant instruments are:
- security-of-supply and information-security requirements in defence tenders, including supply chain disclosure and change control for subcontractors;
- sanctions law, including the restrictions on Russian content and subcontractors;
- the telecommunications-specific framework for high-risk 5G vendors;
- NIS-2 supply chain security duties from October 2026, which force in-scope companies to manage supplier cyber risk contractually; and
- FDI screening at the ownership level.
Enforcement is contract-based in procurement, and administrative or criminal under sanctions and export control law. In practice, contracting authorities increasingly require the mapping of critical sub-tier suppliers during tender procedures.
5.7 Counter-Espionage and Insider Threat Obligations
There is no standalone counter-espionage compliance statute for companies. Holders of facility security clearances must implement the required protective measures, appoint security officers and report security-relevant incidents to the competent authority, the Federal Ministry of Defence and Abwehramt for defence contracts and otherwise the Directorate for State Protection and Intelligence; the loss or compromise of classified material triggers immediate reporting duties under the security annex.
The Criminal Code penalises intelligence activity to Austria’s detriment. The long-debated gap whereby espionage conducted from Austrian soil against foreign states or international organisations is largely not punishable has led to reform plans; the progress of such plans should be verified at the time of reading. Structured insider threat programmes are contractual best practice rather than a statutory duty.
5.8 Foreign Ownership, Control and Influence (FOCI) Mitigation
Austria has no formal FOCI mitigation system comparable to US special security agreements, proxy boards or government-appointed security directors. The underlying risk is addressed through three instruments:
- first, FDI screening under the Investment Control Act, where clearance can be made subject to behavioural or structural conditions – for example, ring-fencing of sensitive information, governance undertakings or the maintenance of capabilities in Austria;
- second, the facility security clearance process, in which foreign ownership and control are assessed and can bar access to classified contracts; and
- third, contract-level requirements such as security annexes and personnel restrictions.
These instruments operate on a case-by-case basis; there is no standing register of mitigation agreements.
5.9 Interaction Between National Security Regulation and Other Regimes
The national security instruments interlock with the other regimes rather than override them. A single transaction can simultaneously trigger FDI screening under the Investment Control Act, merger control, export control consequences for the transfer of technology to the acquirer, the reassessment of facility clearances and consequences under ongoing classified contracts.
In procurement, national security appears in three functions: as an exemption ground (Article 346, TFEU), as an exclusion ground (reliability of the bidder) and as a contract condition (security of supply and of information). Sanctions law overlies all of these regimes. The instruments are administered by different ministries with formal agreement requirements, and there is no one-stop shop; parallel workstreams and the early sequencing of filings are therefore essential in transactions and major programmes.
6. M&A, Joint Ventures and Foreign Direct Investment in the Defence Sector
6.1 FDI Screening Legislation and Regulatory Framework
The Investment Control Act, in force since July 2020, governs the screening of FDI; the competent authority is the Federal Ministry for Economy, supported by an inter-ministerial committee, and the EU co-operation mechanism under Regulation (EU) 2019/452 (the “FDI Screening Regulation”) applies.
The regime covers acquisitions by natural or legal persons from outside the EU, the EEA and Switzerland of Austrian undertakings active in fields relevant to security or public order. Defence goods and defence technologies, as well as the operation of critical infrastructure, belong to the particularly sensitive sectors specified in Part 1 of the Annex to the Investment Control Act, which attract the lowest trigger thresholds. Micro-enterprises with fewer than ten employees and less than EUR2 million in turnover are exempt.
6.2 Transactions Subject to FDI Screening
The transactions that are subject to FDI screening are: direct or indirect acquisitions of shares reaching 10% of the voting rights in the particularly sensitive sectors, including defence, and otherwise 25% or 50%; acquisitions of a controlling influence; acquisitions of essential assets of a covered undertaking; and the establishment of joint ventures where this confers the relevant influence. The acquisition of decisive influence by other means is equally covered.
The 10% threshold means that even minority investments in defence-related targets are notifiable. There are no transaction value thresholds; the test is the combination of sector and influence. Intra-group restructurings can be caught where the ultimate acquirer is a third-country person.
6.3 Mandatory vs Voluntary Notification
Notification is mandatory and must occur before closing; the transaction may not be implemented until approval has been granted (standstill obligation). The obligation to file lies with the acquirer; the target must notify where it becomes aware of the transaction and no filing has been made.
Closing without clearance is a criminal offence punishable by imprisonment, with higher penalties where clearance was obtained on the basis of false information, and the transaction remains provisionally ineffective under civil law until its approval. Where it is unclear whether a filing obligation exists, an application for a certificate of non-objection (Unbedenklichkeitsbescheinigung) is the practical route to certainty.
6.4 Review Process and Timetable
The filing to the Federal Ministry for Economy must contain details on the acquirer, including details on the ownership chain up to the ultimate beneficial owner, funding sources and any government links, on the target and its activities, and on the transaction structure. The EU co-operation mechanism is run first; Phase 1 then allows one month for the decision to clear or to open an in-depth review, and Phase 2 allows a further two months for approval, conditional approval or prohibition.
The standstill obligation applies throughout. In practice, information requests extend the overall duration; straightforward defence-adjacent cases complete in roughly two to three months; complex cases take significantly longer.
6.5 Assessment Criteria
The substantive test of whether a transaction poses a national security risk is whether the acquisition may endanger security or public order within the meaning of Articles 52 and 65, TFEU. The statutory factors mirror Article 4 of the FDI Screening Regulation: effects on critical infrastructure and critical technologies, expressly including dual-use items, on the supply of critical inputs and on access to sensitive information, as well as acquirer-related factors such as state control or state funding, prior involvement in activities affecting security, and the risk of illegal or criminal activities.
Defence-specific considerations include access to classified information and defence technology, the dependence of the Austrian Armed Forces or of co-operative programmes on the target’s supplies, and the risk of technology leakage through the acquirer’s group.
6.6 Conditions, Remedies and Prohibition
Clearance may be granted subject to conditions, which can be behavioural or structural: protection of classified information and know-how; retention of capabilities, research or production in Austria; supply commitments towards Austrian authorities; and governance measures such as information barriers or restrictions on the acquirer’s access to defined business areas.
Prohibition is available where conditions cannot remove the danger, and transactions implemented in breach of the standstill can be addressed through orders to restore the previous situation, including unwinding. In practice, conditional clearance is the typical outcome in sensitive defence cases; outright prohibitions remain rare.
6.7 Golden Shares and Special Government Rights
Austria does not use golden shares or comparable special government rights in defence companies, and there is no statutory special-rights regime for the sector. Where state influence exists, it flows from ordinary shareholdings, managed through the state holding company in other strategic sectors, and from the regulatory instruments described above: FDI screening, facility security clearances and contract terms.
The restrictive case law of the CJEU on golden shares under the free movement of capital would in any event narrowly confine such instruments; defence-specific special rights would require a genuine justification under Article 346, TFEU.
6.8 Joint Ventures in the Defence Sector
There is no defence-specific joint venture statute; several regimes apply in layers. FDI screening applies where a third-country partner obtains the relevant influence over an Austrian defence business; merger control applies where the thresholds are met; export control applies to any transfer of controlled technology or technical assistance into the joint venture, including intangible transfers to foreign parent personnel; and the classified-information rules apply where the joint venture performs classified contracts, including facility clearances and national personnel requirements.
The allocation of background and foreground IP is contractual. Government customers commonly require usage rights for maintenance and further development, and EU-funded projects impose their own rules on results and access rights. Licensing arrangements with export control flow-downs are the standard mechanism for technology transfer.
6.9 Interaction with Competition/Antitrust Review
FDI screening and merger control run in parallel and independently: the Investment Control Act procedure before the Federal Ministry for Economy, and merger control before the Federal Competition Authority and the Cartel Court or, for transactions with an EU dimension, before the European Commission. There is no statutory co-ordination mechanism; the parties must align the timing themselves, and the standstill obligations are cumulative.
For EU-dimension mergers, Article 21(4) of the EU Merger Regulation (Council Regulation (EC) No 139/2004) permits Austria to take measures to protect legitimate interests, including public security, alongside the Commission’s competition review, and Article 346, TFEU can additionally shield genuine defence aspects. National security review may not be used to pursue competition objectives, and vice versa; in defence transactions, the security conditions are typically the binding constraint.
7. Investigations and Litigation in the Defence Sector
7.1 Principal Investigative Authorities
On the criminal side, the public prosecutors direct investigations executed by the criminal police; the Economic Crime and Corruption Prosecutor’s Office handles corruption and major economic cases, including procurement-related bribery and serious export control or sanctions matters; the Directorate for State Protection and Intelligence covers state-protection aspects; and the Austrian Customs Office enforces customs and export control law.
On the administrative side, the Federal Ministry for Economy supervises compliance with the Foreign Trade Act 2011, the Financial Market Authority has supervised financial sanctions compliance since 2026, and the Federal Competition Authority investigates bid rigging. The Court of Audit examines the economy and regularity of defence procurement; it has no enforcement powers but high practical impact, and parliamentary committees of inquiry have repeatedly examined defence procurement. Investigative powers derive from the Code of Criminal Procedure and the respective administrative statutes.
7.2 Triggers for Investigation
Typical triggers for regulatory investigation are audit findings of the Court of Audit, customs findings at export, whistle-blower reports through internal channels or to the Federal Bureau of Anti-Corruption, suspicious-transaction and freezing reports from financial institutions, referrals between authorities, media and parliamentary scrutiny, and information from foreign partner authorities.
As to mandatory reporting: public officials must report suspected criminal offences arising within their sphere of competence; freezing measures must be reported under sanctions law; and, from October 2026, significant cyber incidents must be reported under the Network and Information System Security Act 2026. Companies have no general duty of criminal self-disclosure; export licence holders must, however, report certain irregularities and changed circumstances to the licensing authority.
7.3 Investigative Powers and Procedures
Under the Code of Criminal Procedure, prosecutors can order the production of documents and data, seizure, the questioning of suspects and witnesses, the disclosure of account information and, for serious offences, covert surveillance measures; searches require court authorisation. Administrative authorities hold information and inspection rights: the Federal Ministry for Economy can audit export licence holders, and the Financial Market Authority can conduct on-site inspections.
For classified material, protections operate through restricted file access, the exclusion of the public from hearings and the Information Security Act framework; investigating authorities requiring access to classified information co-ordinate with the originating authority. Cross-border defence cases add the complexity of mutual legal assistance and of evidence located abroad.
7.4 Dawn Raids and Unannounced Inspections
Searches of business premises require a prosecutor’s application and court approval and are executed by the criminal police, frequently unannounced; the Financial Market Authority and the Federal Competition Authority also conduct on-site measures within their remits.
The rights of the entity under investigation include service of the search order; the presence of a representative and the right to call counsel, although the search need not await counsel’s arrival; and an objection procedure for materials claimed to be privileged, which are then sealed and reviewed by the court. The entity must tolerate the search and must not destroy evidence or obstruct the measure; co-operation beyond toleration is voluntary. The preparation of a dawn raid protocol is a standard compliance measure for defence contractors.
7.5 Legal Professional Privilege and Confidentiality
Communications with external Austrian attorneys are protected through the attorney’s right to professional secrecy and the corresponding right to refuse testimony, which extends to documents in the attorney’s custody and, under the circumvention prohibition, to corresponding materials seized at the premises or home of the client; the sealing procedure with judicial review secures contested items. In-house counsel do not enjoy attorney privilege in Austria.
There is no national-security exception abolishing privilege. Classified information in counsel’s hands remains, however, subject to the Information Security Act regime, and security clearances may be required for work on classified defence files. In EU competition investigations, the narrower EU privilege standards apply.
7.6 Debarment and Exclusion from Future Procurement
Final convictions for catalogue offences (ie, the offences exhaustively listed in the statute, such as corruption, fraud, money laundering and participation in a criminal organisation) trigger mandatory exclusion from procurement procedures, in general for five years from the conviction; discretionary grounds such as grave professional misconduct, including established competition or export control violations, support exclusion for up to three years following the relevant event. There is no central debarment list; each contracting authority assesses eligibility in its own procedure.
Self-cleaning is expressly recognised and can be demonstrated by means of compensation of the damage caused, active co-operation in clarifying the facts, and concrete technical, organisational and personnel measures. The adequacy of the measures is assessed in proportion to the misconduct, and successful self-cleaning restores eligibility even within the exclusion periods.
7.7 Civil Litigation and Dispute Resolution
There are no specialist forums for the resolution of disputes arising from defence contracts. Contract disputes go to the ordinary civil courts, in Vienna typically the Commercial Court; the state can and does agree arbitration in major defence contracts, with Vienna as an established seat and the Vienna International Arbitral Centre as an established forum, which also facilitates confidentiality. Procurement review lies with the Federal Administrative Court.
Classified information in litigation is handled through the exclusion of the public, restrictions on file access and careful drafting of submissions; Austria has no statute comparable to classified-procedures legislation in other jurisdictions, which makes protective case management agreements important. Settlements are common where a dispute would otherwise force the disclosure of sensitive programme details.
7.8 Whistleblower Protections
The Whistleblower Protection Act (HinweisgeberInnenschutzgesetz), in force since 2023, implements the EU Whistleblowing Directive (Directive (EU) 2019/1937). Companies with 50 or more employees must operate internal reporting channels; external reports can be made to the Federal Bureau of Anti-Corruption as the central external channel or to sectoral regulators. Protections include the prohibition of retaliation and a shifted burden of proof in retaliation disputes.
Defence-specific caveats apply: information covered by classification rules and by national security, and procurement falling within the defence and security exclusions of the Directive, are outside the protected scope, and official secrecy and intelligence offences continue to apply. Reporters of corruption in defence procurement remain protected where no classified information is disclosed.
7.9 Corporate Criminal Liability
Under the Corporate Criminal Liability Act, legal entities are responsible for criminal offences, including export control, sanctions and bribery offences, committed by decision-makers, or by employees where the offence was made possible or substantially facilitated by a failure of supervision or organisation.
The sanctions for such offences are corporate fines structured in daily rates, up to 180 daily rates with the rate determined by the entity’s earnings situation, alongside the skimming of proceeds and, in procurement, exclusion consequences. Prosecutors have discretion whether to pursue an entity; effective compliance programmes, self-reporting and remediation weigh against prosecution and reduce the fine. The individual liability of managers runs in parallel.
Schiefer Rechtsanwälte GmbH
Rooseveltplatz 4-5/5
1090 Vienna
Austria
+43 1 402 68 28
office@schiefer.at www.schiefer.at
Law and Practice in Austria
Authors
Schiefer Rechtsanwälte GmbH is an Austrian law firm with offices in Vienna and other major cities in Austria, focused on public procurement, defence and dual-use, and banking and finance. The firm advises contracting authorities, bidders, privately-owned companies and credit institutions across the full project life cycle, from strategy and tender design through award to contract performance and review proceedings. In the defence sector, the firm advises on major equipment programmes, government-to-government arrangements, industrial co-operation and security-of-supply structures, as well as on the export control, sanctions and investment screening questions arising in defence supply chains. Recent work includes acting as lead adviser on the industrial co-operation programme of Austria with Italian defence contractor Leonardo. The firm publishes regularly on procurement, defence regulation and defence financing.